AI-Generated Code Poses Major Security Risks in Nearly Half of All Development Tasks, Veracode Research Reveals
30.7.2025 13:50:00 CEST | Business Wire | Press release
Comprehensive Analysis of More Than 100 Large Language Models Exposes Security Gaps: Java Emerges as Highest-Risk Programming Language, While AI Misses 86% of Cross-Site Scripting Threats
Veracode, a global leader in application risk management, today unveiled its 2025 GenAI Code Security Report, revealing critical security flaws in AI-generated code. The study analyzed 80 curated coding tasks across more than 100 large language models (LLMs), revealing that while AI produces functional code, it introduces security vulnerabilities in 45 percent of cases.
This press release features multimedia. View the full release here: https://www.businesswire.com/news/home/20250730694951/en/
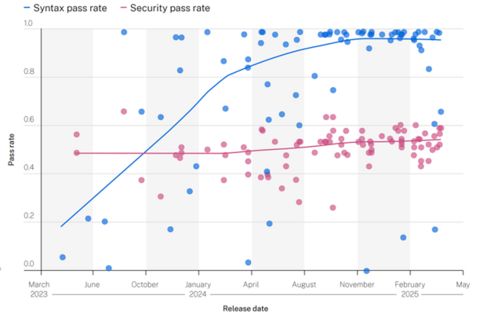
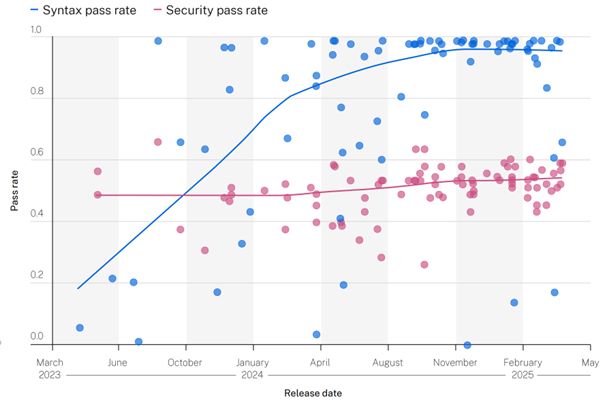
Security and Syntax Pass Rates vs LLM Release from the Veracode 2025 GenAI Code Security Report
The research demonstrates a troubling pattern: when given a choice between a secure and insecure method to write code, GenAI models chose the insecure option 45 percent of the time. Perhaps more concerning, Veracode's research also uncovered a critical trend: despite advances in LLMs’ ability to generate syntactically correct code, security performance has not kept up, remaining unchanged over time.
“The rise of vibe coding, where developers rely on AI to generate code, typically without explicitly defining security requirements, represents a fundamental shift in how software is built,” said Jens Wessling, Chief Technology Officer at Veracode. “The main concern with this trend is that they do not need to specify security constraints to get the code they want, effectively leaving secure coding decisions to LLMs. Our research reveals GenAI models make the wrong choices nearly half the time, and it’s not improving.”
AI is enabling attackers to identify and exploit security vulnerabilities quicker and more effectively. Tools powered by AI can scan systems at scale, identify weaknesses, and even generate exploit code with minimal human input. This lowers the barrier to entry for less-skilled attackers and increases the speed and sophistication of attacks, posing a significant threat to traditional security defenses. Not only are vulnerabilities increasing, but the ability to exploit them is becoming easier.
LLMs Introduce Dangerous Levels of Common Security Vulnerabilities
To evaluate the security properties of LLM-generated code, Veracode designed a set of 80 code completion tasks with known potential for security vulnerabilities according to the MITRE Common Weakness Enumeration (CWE) system, a standard classification of software weaknesses that can turn into vulnerabilities. The tasks prompted more than 100 LLMs to auto-complete a block of code in a secure or insecure manner, which the research team then analyzed using Veracode Static Analysis. In 45 percent of all test cases, LLMs introduced vulnerabilities classified within the OWASP (Open Web Application Security Project) Top 10—the most critical web application security risks.
Veracode found Java to be the riskiest language for AI code generation, with a security failure rate over 70 percent. Other major languages, like Python, C#, and JavaScript, still presented significant risk, with failure rates between 38 percent and 45 percent. The research also revealed LLMs failed to secure code against cross-site scripting (CWE-80) and log injection (CWE-117) in 86 percent and 88 percent of cases, respectively.
“Despite the advances in AI-assisted development, it is clear security hasn’t kept pace,” Wessling said. “Our research shows models are getting better at coding accurately but are not improving at security. We also found larger models do not perform significantly better than smaller models, suggesting this is a systemic issue rather than an LLM scaling problem.”
Managing Application Risks in the AI Era
While GenAI development practices like vibe coding accelerate productivity, they also amplify risks. Veracode emphasizes that organizations need a comprehensive risk management program that prevents vulnerabilities before they reach production—by integrating code quality checks and automated fixes directly into the development workflow.
As organizations increasingly leverage AI-powered development, Veracode recommends taking the following proactive measures to ensure security:
- Integrate AI-powered tools like Veracode Fix into developer workflows to remediate security risks in real time.
- Leverage Static Analysis to detect flaws early and automatically, preventing vulnerable code from advancing through development pipelines.
- Embed security in agentic workflows to automate policy compliance and ensure AI agents enforce secure coding standards.
- Use Software Composition Analysis(SCA) to ensure AI-generated code does not introduce vulnerabilities from third-party dependencies and open-source components.
- Adopt bespoke AI-driven remediation guidance to empower developers with precise fix instructions and train them to use the recommendations effectively.
- Deploy a Package Firewall to automatically detect and block malicious packages, vulnerabilities, and policy violations.
“AI coding assistants and agentic workflows represent the future of software development, and they will continue to evolve at a rapid pace,” Wessling concluded. “The challenge facing every organization is ensuring security evolves alongside these new capabilities. Security cannot be an afterthought if we want to prevent the accumulation of massive security debt.”
The complete 2025 GenAI Code Security Report is available to download on the Veracode website.
About Veracode
Veracode is a global leader in Application Risk Management for the AI era. Powered by trillions of lines of code scans and a proprietary AI-assisted remediation engine, the Veracode platform is trusted by organizations worldwide to build and maintain secure software from code creation to cloud deployment. Thousands of the world’s leading development and security teams use Veracode every second of every day to get accurate, actionable visibility of exploitable risk, achieve real-time vulnerability remediation, and reduce their security debt at scale. Veracode is a multi-award-winning company offering capabilities to secure the entire software development life cycle, including Veracode Fix, Static Analysis, Dynamic Analysis, Software Composition Analysis, Container Security, Application Security Posture Management, Malicious Package Detection, and Penetration Testing.
Learn more at www.veracode.com, on the Veracode blog, and on LinkedIn and X.
Copyright © 2025 Veracode, Inc. All rights reserved. Veracode is a registered trademark of Veracode, Inc. in the United States and may be registered in certain other jurisdictions. All other product names, brands or logos belong to their respective holders. All other trademarks cited herein are property of their respective owners.
View source version on businesswire.com: https://www.businesswire.com/news/home/20250730694951/en/
Subscribe to releases from Business Wire
Subscribe to all the latest releases from Business Wire by registering your e-mail address below. You can unsubscribe at any time.
Latest releases from Business Wire
SES Launches Cash Tender Offer28.9.2026 13:21:00 CEST | Press release
THIS ANNOUNCEMENT RELATES TO THE DISCLOSURE OF INFORMATION THAT QUALIFIED OR MAY HAVE QUALIFIED AS INSIDE INFORMATION WITHIN THE MEANING OF ARTICLE 7(1) OF THE MARKET ABUSE REGULATION (EU) 596/2014. NOT FOR RELEASE, PUBLICATION OR DISTRIBUTION IN OR INTO OR TO ANY PERSON LOCATED OR RESIDENT IN, OR AT ANY ADDRESS IN, THE UNITED STATES OF AMERICA, ITS TERRITORIES AND POSSESSIONS (INCLUDING PUERTO RICO, THE U.S. VIRGIN ISLANDS, GUAM, AMERICAN SAMOA, WAKE ISLAND AND THE NORTHERN MARIANA ISLANDS), ANY STATE OF THE UNITED STATES OF AMERICA OR THE DISTRICT OF COLUMBIA (THE UNITED STATES) OR TO ANY U.S. PERSON (AS DEFINED IN REGULATION S OF THE UNITED STATES SECURITIES ACT OF 1933, AS AMENDED (THE SECURITIES ACT)) OR IN OR INTO ANY JURISDICTION WHERE IT IS UNLAWFUL TO RELEASE, PUBLISH OR DISTRIBUTE THIS ANNOUNCEMENT (SEE “OFFER AND DISTRIBUTION RESTRICTIONS” BELOW). SES (the “Offeror”) announces today that it is inviting holders of its outstanding €500,000,000 0.875 per cent. Guaranteed Notes
Horizon3 Earns Cyber Essentials Certification Covering NodeZero EU Network28.9.2026 10:00:00 CEST | Press release
Certification provides a defined security baseline for the network supporting Horizon3’s EU data sovereignty site in Germany Horizon3, the AI-Native Proactive Security Company, today announced that it has earned Cyber Essentials Plus certification covering its NodeZero AWS EU network. The network supports Horizon3’s EU data sovereignty site in Germany. This press release features multimedia. View the full release here: https://www.businesswire.com/news/home/20260928143792/en/ Horizon3 Earns Cyber Essentials Certification Covering NodeZero EU Network Organizations use NodeZero® to test production environments and find weaknesses attackers can exploit. When customers and partners assess the platform itself, they also need to understand the security standards applied to its supporting infrastructure. The Cyber Essentials certificate identifies a defined portion of that infrastructure and the baseline against which it was assessed. Developed by the UK’s National Cyber Security Centre, Cybe
Thales Expands Collaboration with Google Cloud to Help Secure Agentic AI Workflows28.9.2026 09:03:00 CEST | Press release
Integration enables new protections for communications between AI agents, models, enterprise data, and tools to help control what agents can access, share, and do Thales AI Security Fabric mitigates risks, brings enhanced visibility and policy enforcement to AI-driven workflows on Google Cloud Thales today announced an expanded collaboration with Google Cloud to help enterprises address emerging security and governance challenges associated with agentic AI, bringing integrated protection, visibility, and policy enforcement to AI-driven workflows on Google Cloud. This press release features multimedia. View the full release here: https://www.businesswire.com/news/home/20260928647188/en/ ©Thales The integration of Thales AI Security Fabric with Google Cloud Gemini Enterprise helps organizations apply security, governance, and visibility across interactions among users, agents, models, and tools in real time. “Enterprises are moving from AI assistants to AI agents that can autonomously ta
SPORVIGILANCE Targets Safer Medicines and Billion-Euro Savings for Global Pharma Facing EU IDMP Fines28.9.2026 08:13:00 CEST | Press release
British regulatory technology company SPORVIGILANCE is targeting one of global pharma’s major compliance challenges with a platform offering a faster route to IDMP and SPOR readiness, compliance and governance. As the European Medicines Agency advances structured medicinal product data, companies face pressure to keep regulatory data accurate, standardised and aligned with EMA requirements. SPORVIGILANCE replaces fragmented manual assessment with a regulatory intelligence layer built around IDMP, SPOR and Product Management Service (PMS) requirements. At its core is an IDMP Business Rule Validation Engine that assesses medicinal product data at scale and at field level, identifying missing, inconsistent and non-compliant data. SPORVIGILANCE is the only platform to translate IDMP business rules directly into automated validation logic, enabling companies to test data against the rules rather than rely on manual interpretation. Its PMS Alignment capability reconciles internal RIM data ag
Sofinnova Partners Closes Oversubscribed €82 Million Sofinnova MD Start IV Fund to Create the Next Generation of Medtech Companies28.9.2026 08:00:00 CEST | Press release
The new fund extends Sofinnova’s 20-year track record of company creation with capacity to launch six to eight new ventures across Europe and the US Sofinnova Partners ("Sofinnova"), a leading European life sciences venture capital firm based in Paris, London, and Milan, today announced the final close of Sofinnova MD Start IV at €82 million. The fund, which was oversubscribed, will help expand Sofinnova's medtech company-creation strategy across Europe and the US with greater capacity to launch new ventures and support them through key stages of development. With plans to launch six to eight new medtech companies over the next five years, Sofinnova MD Start IV will support ventures from inception through key clinical and operational milestones, providing founders with both capital and hands-on support. Sofinnova MD Start's approach combines clinical insight, entrepreneurial talent, and operational expertise to tackle significant unmet medical needs. The previous fund, Sofinnova MD Sta
In our pressroom you can read all our latest releases, find our press contacts, images, documents and other relevant information about us.
Visit our pressroom